Kelly Liyakasa contributed
The European Union’s General Data Protection Regulation (GDPR) will become law in May 2018.
Think it won’t affect you? Think again.
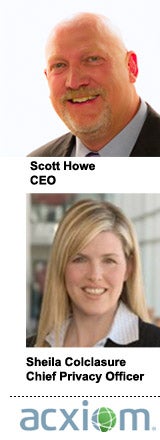
“This kind of legislation impacts every company in the world,” said Acxiom CEO Scott Howe. “Very few companies aren’t collecting or utilizing information to improve their decision making.”
But how the GDPR regulates data across Europe – and how exactly it will affect US companies – isn’t entirely set.
“There’s a considerable amount of work left to do on the delegated acts to clarify how the law will take effect,” said Sheila Colclasure, Acxiom’s global chief privacy officer.
Even with those uncertainties, however, GDPR is still a big deal and will set the tone for data protection regulation globally, Colclasure said.
The stakes are incredibly high for companies that fail to comply. If a European court decides a company has played fast and loose with consumer data, that company could be fined up to 4% of its global annual revenue under the GDPR. And that’s for a single infraction.
AdExchanger spoke with Colclasure and Howe about the coming legislation and its likely impact.
AdExchanger: So, I guess this isn’t a big nothing burger, like Do Not Track.
SCOTT HOWE: Companies can’t afford to have a different data policy in every country and every state. You need a framework across the world and [to] shoot for the highest common denominator. In any regulated industry, the complexity will kill you, so you have to aim for that highest common denominator.
But it varies so much. The common example is that IP address isn’t PII in the US, but it’s PII in Germany.
SHEILA COLCLASURE: We keep bumping into this data interoperability dilemma. It’s hard to operate in the global economy when you don’t have geographical borders in digital.
We used to have the EU-US Safe Harbor. That failed, and it was replaced by the Privacy Shield, which was designed to establish a means by which data can legally transfer out of Europe into the US. It will be reviewed this fall. But this forced globalization is an issue around the world. Countries like Russia, for instance, are siloing themselves and constraining their economy because data is an economic issue.
Who has influence over how these regulations will be carried out? Do advertisers and marketers have any say, or is it strictly EU regulators?
SC: Every country has a data protection authority. And Germany has about 15, because they do it on a localized basis. In Europe, there’s friction between the body of data regulation and the economists, who understand that data fuels the economy. So, there’s friction between these two bodies in Europe that remains unresolved.
At Acxiom, we engage the regulators directly to help fill in the white space. How do we show legitimate interest in the law? We write a methodology, we work in coalition with groups like the Information Accountability Foundation, Future of Privacy Forum, FEDMA, all who have voices in the European regulatory community.
What questions must be answered before the GDPR gets implemented next year?
SC: We don’t have full clarity on what GDPR’s requirements are. We have guidance on how to implement coming out from the Data Protection Authorities and Article 29 Working Party and commentary from the European Data Protection supervisor, but it’s still very much in play.
In GDPR, there’s a thing called legitimate interest. And that is one of the pieces of the law we care most about. Legitimate interest is the idea that data fuels the economy. If you use data within the scope of what the consumer might expect, that’s legitimate interest.
There’s another body of law called ePrivacy Regulation that’s more digitally focused around things like cookie IDs and IP addresses. It’s an update of the old European cookie law, and it’s coming into force in May 2018, too. But we believe it will be postponed because it is even murkier than GDPR.
Is there overlap between ePrivacy Regulation and GDPR?
SC: EPrivacy Regulation is consent-driven. You can’t do anything with data until you get consent.
Companies are always thinking about new products and services fueled by data, but under ePrivacy Regulations, you have to think of all of the [consumer privacy] implications up front and drop them into a privacy policy.
With GDPR, legitimate interest does the balancing.
Where is it hardest to find common ground with consumer-interest groups?
SC: I can’t single out one thing. But GDPR is so important because it will be a fully baked body of law and a standard the world over, and its development is highly complex. You have nationalists that are very anti-American. There are certain data protection authorities who would like data about European citizens to stay in-country. That doesn’t acknowledge the global nature of data today.
Will GDPR affect what happens in the US?
SC: There’s millions, if not billions or trillions, of [dollars in] commerce that goes back and forth between Europe and the US. [GDPR] will inform the way we set up our systems, so it needs to be well-written, practical and practicable – meaning companies can do what the law requires.
The EU wants consumers to provide clear, explicit consent. That’s easier said than done, though. Who’s responsible for designing it?
SH: In the next few years, this will become one of the biggest board issues. Every board should be asking their management team: Are you doing this? What are your ethical guidelines? How does this factor into your processes and how you manage the business?
It’s a risk right alongside financial reporting, cybersecurity and ethics. And from the board it must trickle down to every line of business and department. The groundswell will come from the public, as consumers worldwide increasingly voice concerns and regulations worldwide raise visibility even further.
Interview has been edited for clarity